A person decides before your AI agent pays anyone.SignetGate holds each payment call your agent routes through it until a reviewer decides, and refuses it if nobody decides in time.
Every decision is signed, and the record can be checked without us. The first pilots run in shadow mode: an approved call pays nothing, and your payments go through as they do now.
- A fingerprint of the payment
- A fingerprint of the invoice file shown
- The decision, and the account that made it
- Which checks were satisfied
Shown to the reviewer, not signed
- Risk flags
- Confirmation of Payee (simulated)
- The invoice comparison
An agent can pay the wrong account with details that look consistent.
What stalls a pilot is proving which account approved it, what was shown, and that the record hasn’t changed since.
The demo
A gate, a review, and a signed record
Agent
calls a gated tool
Gate
holds the call, captures the invoice
Reviewer
approves or refuses
Signed record
checked later, without us
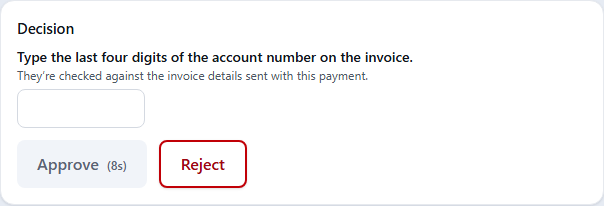

Set up as we specify, a gated payment waits for a reviewer, and if anything goes wrong on the way, the rule is to refuse it, not release it. We fetch the invoice ourselves and show it beside the five details the agent extracted. Riskier payments (a payee we haven’t seen before, an amount over your threshold, or a mismatch) get a longer wait, a recent sign-in, and a typed check, which our server verifies against the invoice data. One whose invoice we couldn’t retrieve can only be refused.
What SignetGate adds to an approval step
Evidence, not a log line
Each decision is signed with Ed25519, including fingerprints of the payment and the exact invoice file shown. Change any signed value and the check fails.
Checkable without us
A single page that works with the network off tells your auditor whether a record is genuine, and whether it’s about the payment in front of them.
Catches and misses, counted
We mix synthetic payments with a deliberate, unambiguous error into the queue and count each reviewer’s catches and misses. Looked at on its own, a synthetic payment can’t be told from real work, with narrow exceptions. Synthetic payments are off in the first pilots.
One hook, and the tool stays out of your allow list
SignetGate installs as a pre-tool-use hook in the Claude Agent SDK, and your payment tool itself pays only on an approval the gate recorded for that call. It refuses to start on a configuration that says a gated tool needs no approval, or that gives the hook too little time to wait for one.
import { SignetGate, bindGatedHandler, createPaymentServer, withSignetGate } from '@signetgate/sdk'; const gate = new SignetGate({ apiKey, baseUrl, trustedKeys, onEvent }); // mapCall turns your tool’s arguments into a payment. Only you know// that shape, and returning null for a gated tool is a refusal.const wireTransfer = tool('wire_transfer', 'Pay a supplier', shape, bindGatedHandler(gate, { toolName: 'mcp__ap__wire_transfer', mapCall }, // Pays only on this gate’s approval for this call and this payment. ({ payment, idempotencyKey }) => pay(payment, idempotencyKey))); const ap = createPaymentServer(gate, createSdkMcpServer, { name: 'ap', tools: [wireTransfer] }); const { options, observe } = withSignetGate( { mcpServers: { ap }, env: agentEnv, settingSources: [], strictMcpConfig: true, // The gated tool is absent here, and the mode is left alone. allowedTools: ['Read', 'Grep'], permissionMode: 'default' as const, }, gate, { gatedTools: ['mcp__ap__wire_transfer'], mapCall, paymentSecrets: ['PAYMENT_API_KEY'], // Your own copy of every receipt, approval or refusal, as each decision is made. onReceipt: (receipt) => receiptStore.put(receipt.receiptId, receipt), },); // observe reads each session’s Claude Code version; a session on any version// other than the pinned one has its gated calls refused.for await (const message of query({ prompt, options })) observe(message);Shadow detection cannot see permission rules held in the framework’s settings files, and it cannot see an agent that never installs it. Design partner teams integrate through the SDK and its Claude Agent SDK hook, sent with each release; the first is not published yet. Using another agent framework? Talk to us.
Your auditor does not have to take our word, or our servers
Give the checker a record and our public key, and it answers whether the record is genuine. Give it the payment instruction too, and it answers whether a genuine record is about that payment.
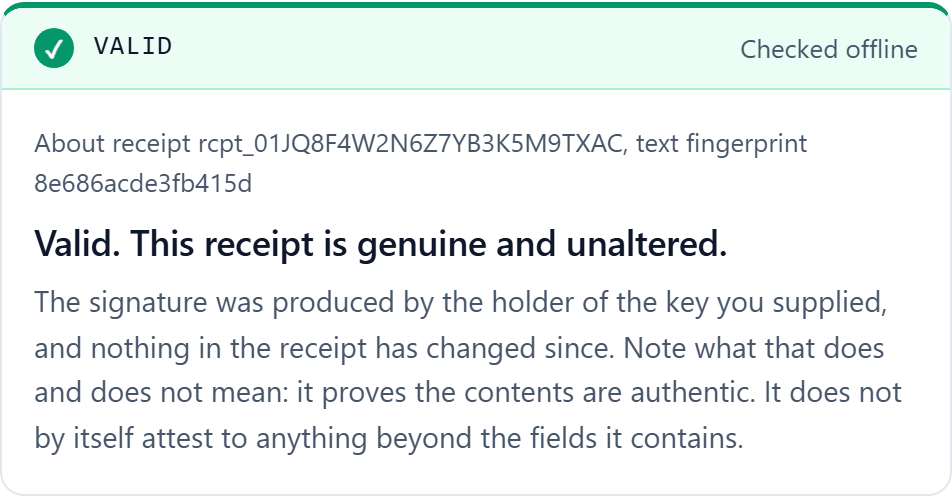
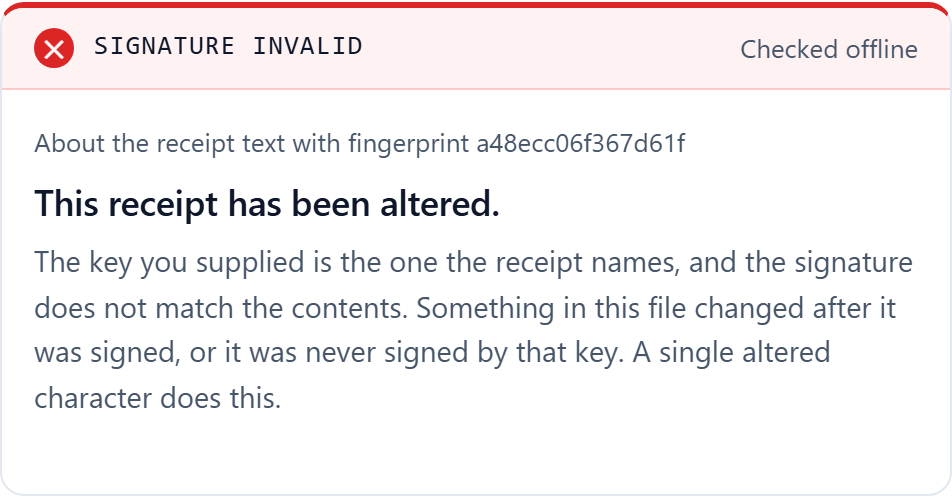
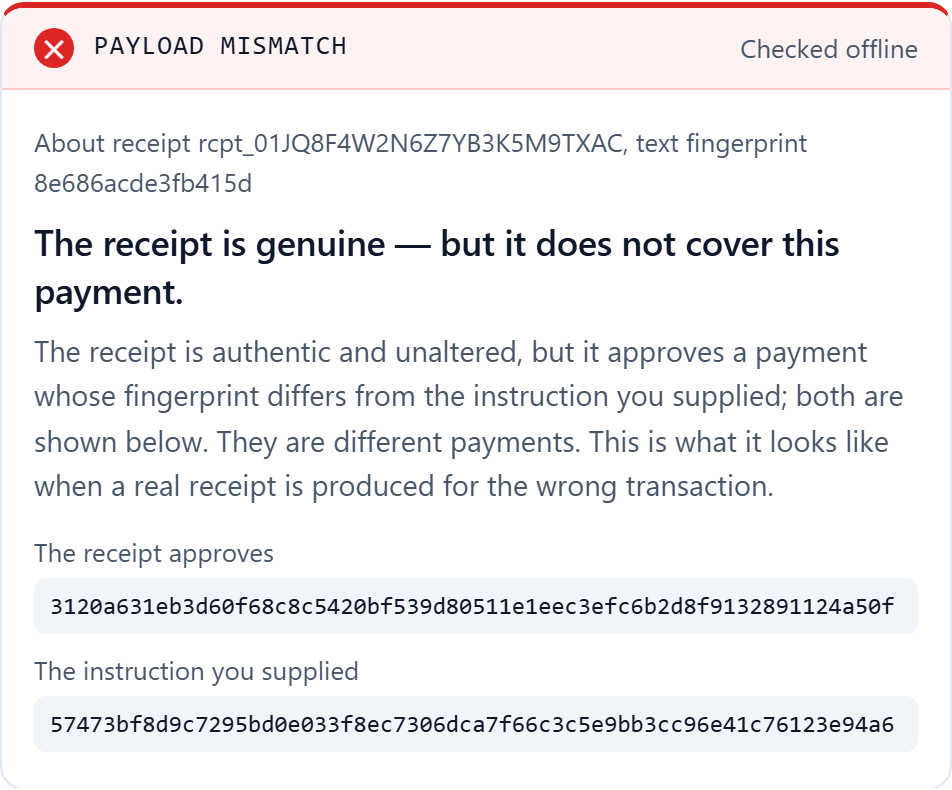
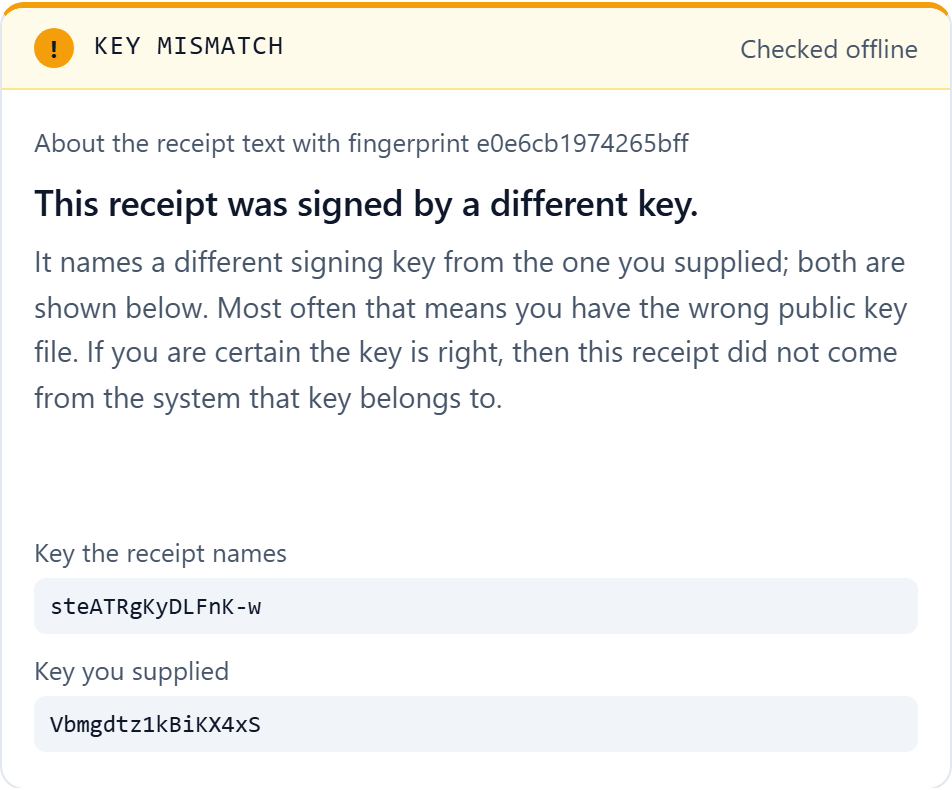
The checker uses the browser’s own signature support, not a library of ours, and self-tests before it judges anything. Keep your own copy of our public key from day one: the check is only as independent as the key you give it.
What it does not do, in short
In this version:
- Reviewers sign in with a username and password, so a record proves which login decided, not who was at the keyboard.
- Confirmation of Payee is simulated, and one reviewer decides.
- A payment that doesn’t go through a gated tool isn’t held.
Before we’d recommend live payments outside a scoped pilot, two things have to land: single sign-on with multi-factor authentication, and a check in the reviewer’s own browser that what it shows is what gets signed. Our known limitations are published in the register, apart from security findings we hold back until they are fixed. Operational detail of the synthetic-payment programme is in the pilot security pack.
A 60-day design partner pilot
We’re taking on a small number of design partners whose AI agents initiate payments. The first pilots run in shadow mode only: approvals move no money, and payments go through as they do now. Pilots on a test account, or under a payment ceiling your payment system enforces, come later.
Keeping your payment credentials out of your agent’s reach stays with you: a payment credential your agent can reach by any route other than the gated payment tool is outside SignetGate’s protection. Our list of limitations says what else stays with you.